Safety Net
Application security that proves its findings
Application security for teams that ship fast. Safety Net rebuilds each application in a sealed sandbox with no internet access, attacks it while watching what it does, and blocks a deployment only when it can show a serious problem is real.
What It Is
Safety Net combines code analysis, an inventory of each application's technology and a test lab. For a deep run it brings the application up in a sealed sandbox with no internet access, then attacks it while watching how it behaves. Findings are graded by evidence, from reported to proven to exploited, and every report lists each check that ran, was skipped or failed, so a clean result means checked rather than ignored.
Two deployment gates sit on top: one asks whether a change could compromise the wider estate, the other whether it leaks secrets or data. A deployment is blocked only by a new, confirmed issue in a defined set of classes; everything else is reported and tracked. Every confirmed finding becomes a rule checked across the whole portfolio, so the same mistake cannot return in another application. Results come as a readable report and plug into code scanning tools and build pipelines.
Inside Safety Net
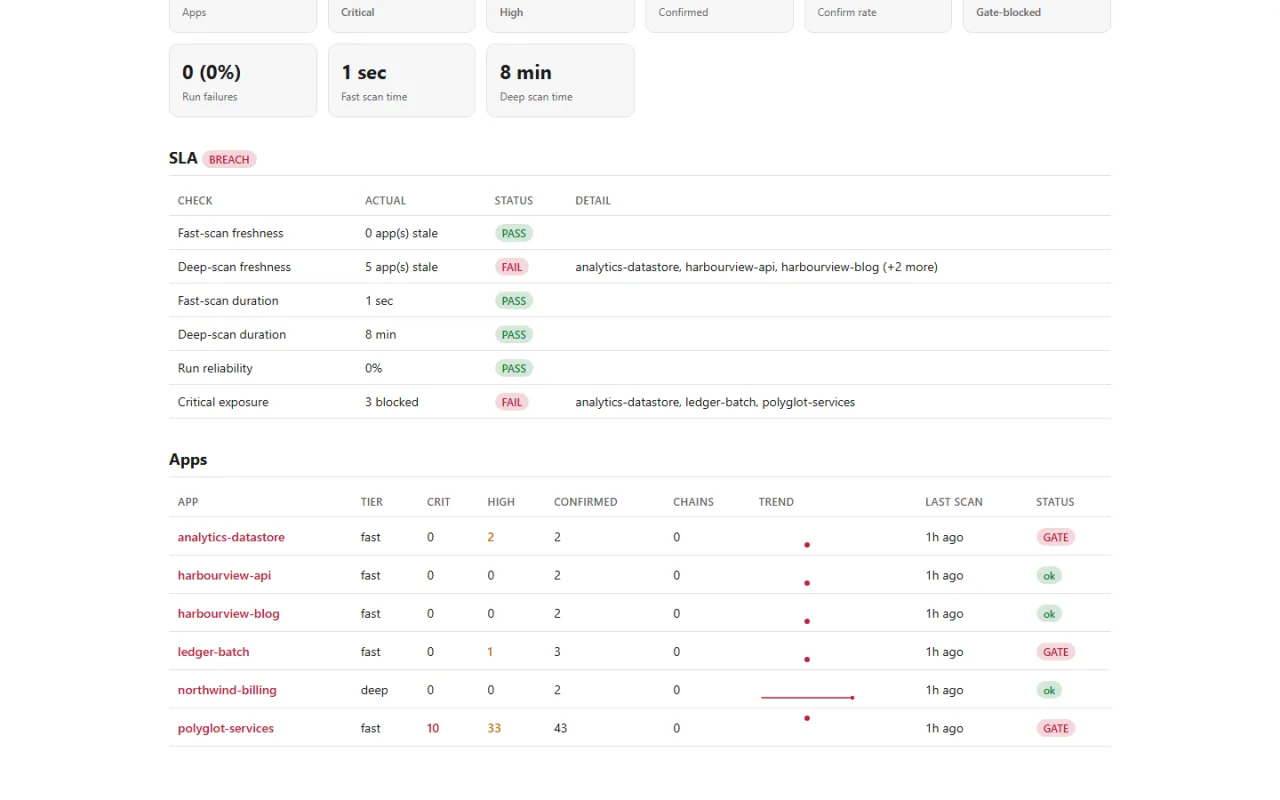
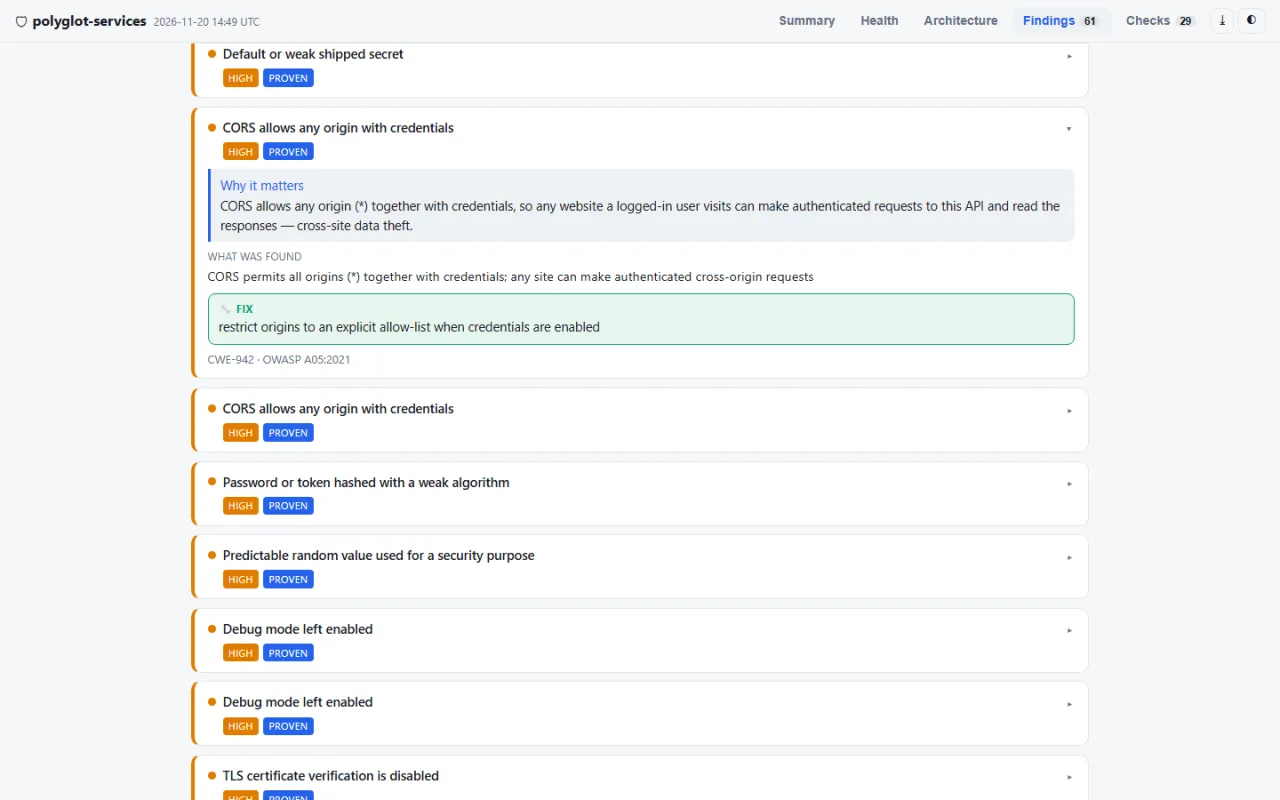
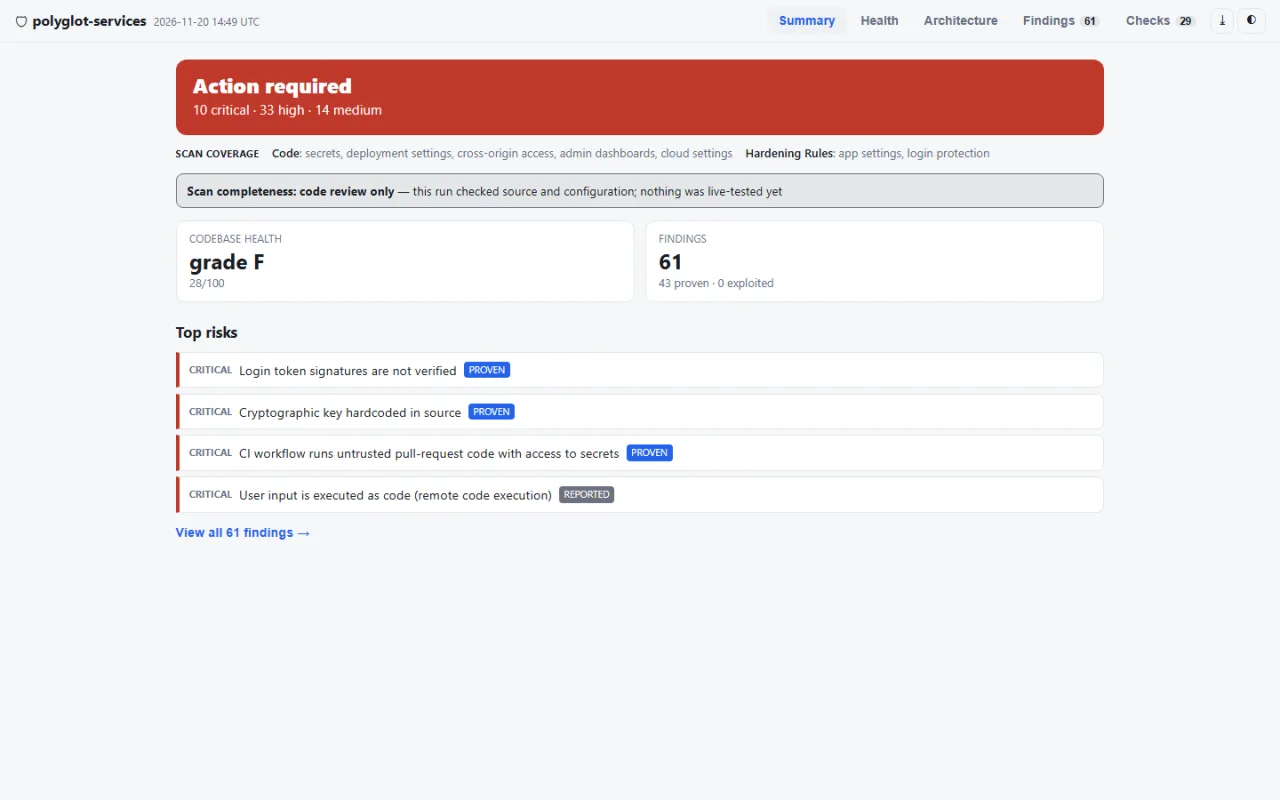
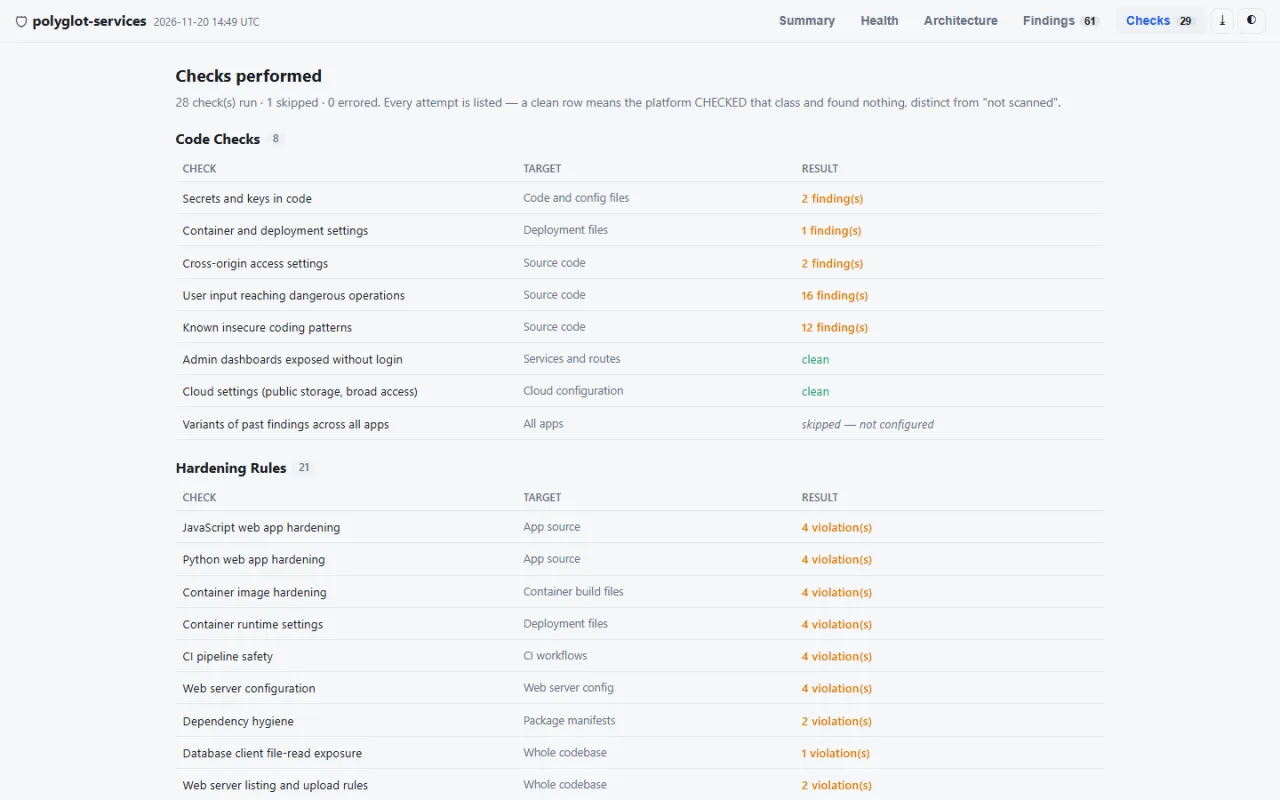
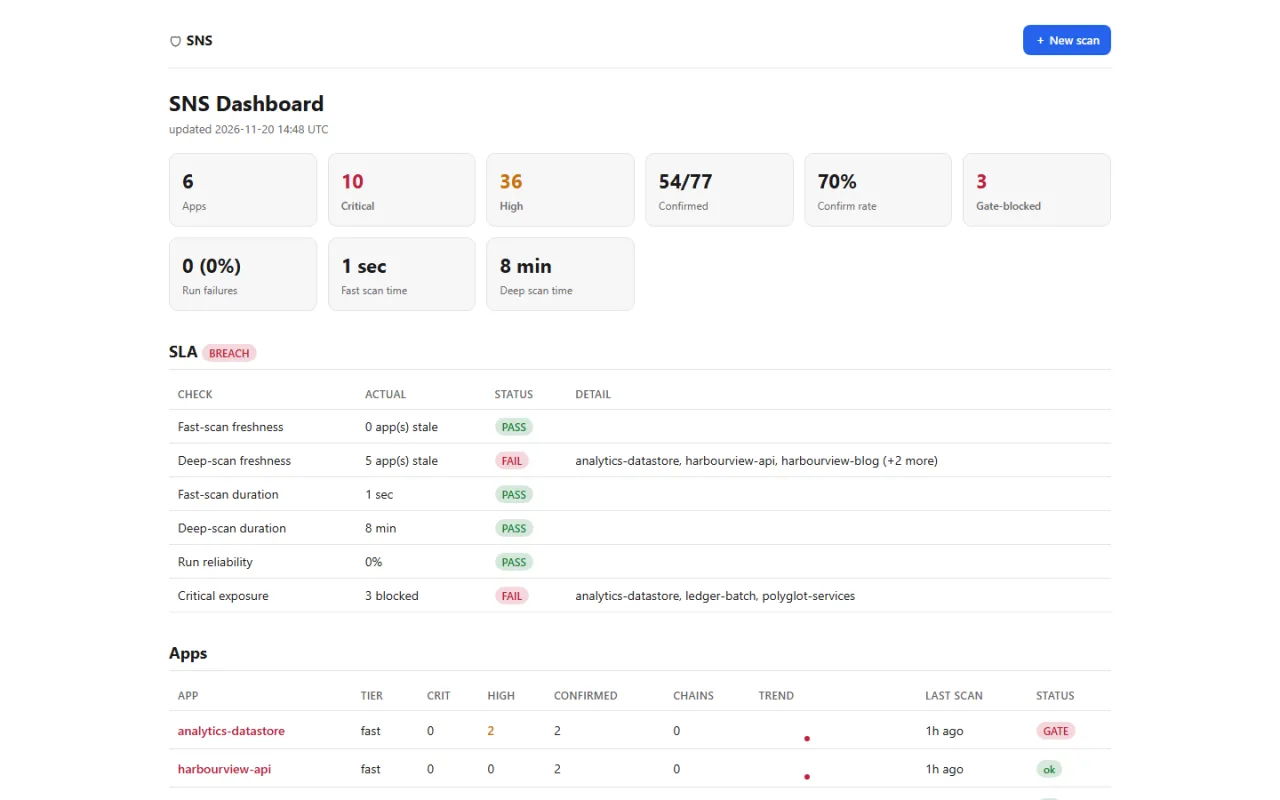
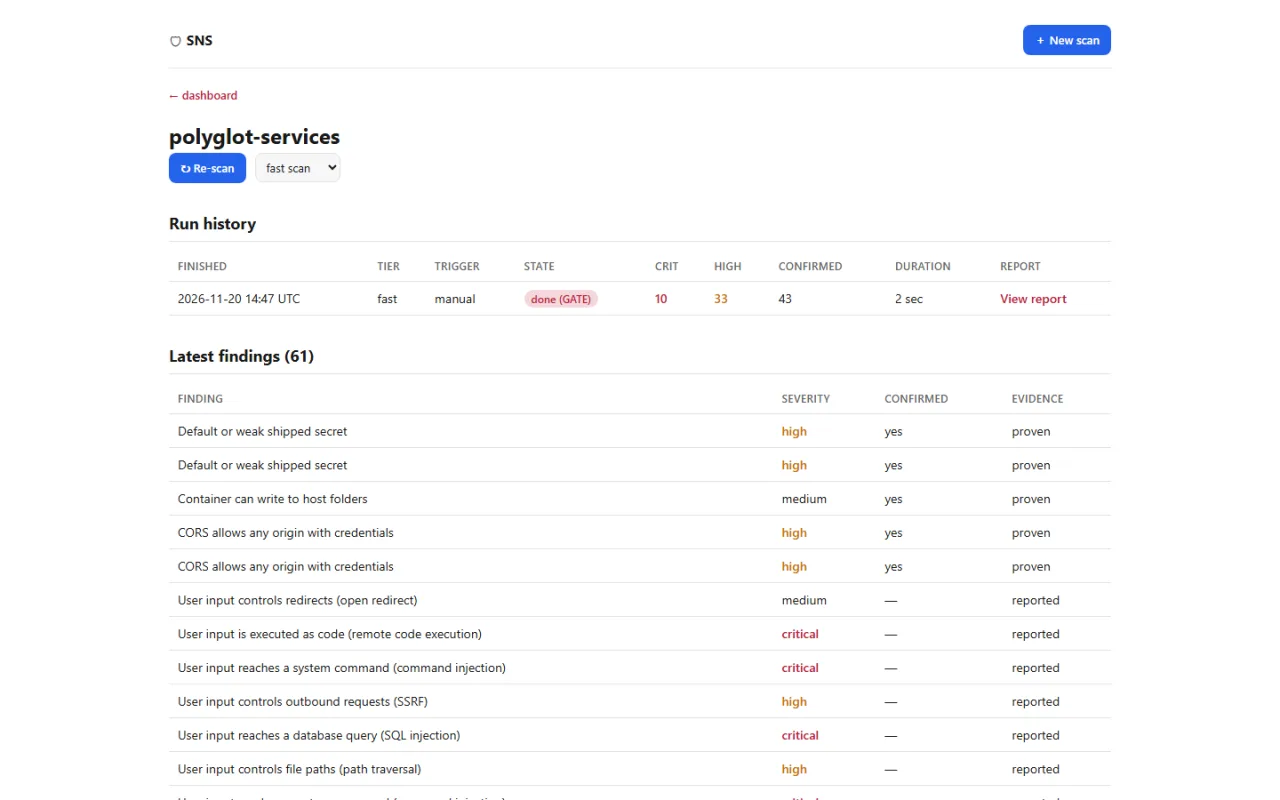
Every screenshot shows demo data: the organisations, people and figures are made up.
Why It Exists
Teams that ship several times a day drown in scanner output: hundreds of possible issues, most of them unreachable, and no way to tell which one matters this afternoon. The result is that people stop reading. Safety Net was built for a technical lead overseeing several independent teams, to answer two questions per deployment with evidence: can this change hurt the rest of the estate, and does it leak anything.
What It Is Worth
Fewer, better findings
Each finding carries its evidence level, location, how to verify it and how to fix it, with CWE and OWASP references, so a developer can act without a security specialist translating.
Gates that teams accept
Blocking only on confirmed, high-impact issues keeps the gate credible; everything below that is visible and ratcheted without stopping the release.
Mistakes fixed once
A confirmed finding becomes an invariant checked across every application, turning one incident into protection for the whole portfolio.
Honest about coverage
Reports state what was checked, what was proven and what still needs the sandbox to confirm, rather than implying completeness.
Who It Helps
Technical leads and CTOs
See security posture across every application on one dashboard, with service levels on scan freshness and critical exposure.
Development teams
Get a fast gate on every change and findings written to be fixed, plugged into GitHub with a ready-made action.
Due diligence and audit
Get evidence-backed reports rather than raw scanner dumps. It is the same thinking we apply in technical due diligence.
At a Glance
| Status | Internal: runs inside Egon Expert Ltd and is not sold on its own; Pilot |
|---|---|
| Evidence levels | Reported, proven, exploited |
| Deployment gates | Blast radius and secret or data leak |
| Scope | The operator's own applications only |
| Built by | Egon Expert Ltd |
Related Products
Need Something Like This?
We build platforms like Safety Net for clients, and help in-house teams build their own. Start with a free 30-minute conversation about what you need.
Book a Free Consultation